Original topic illustration: ChainView BTC866 original topic diagram · ChainView BTC866 Editorial · CC BY 4.0
Publisher and installation source
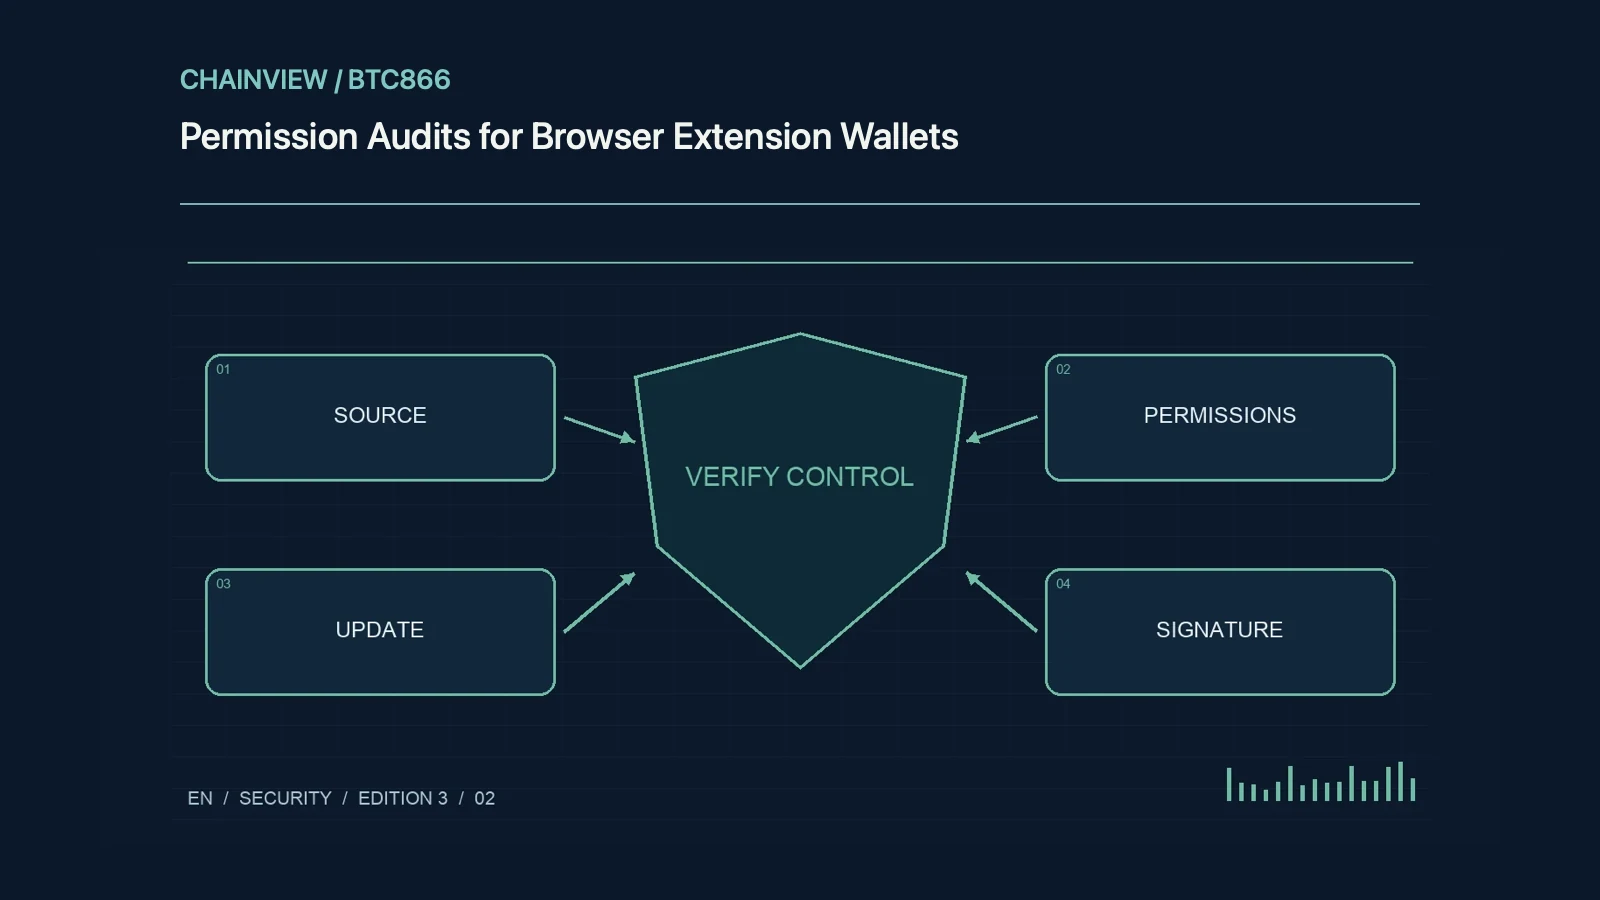
Verify the store link, publisher, and extension identifier through the project's established site. Search ranking, icons, reviews, and download counts are weak provenance evidence. Read requested permissions and retain version details. Store review reduces some distribution risk but cannot guarantee every future update or maintainer account remains safe. Provenance is an ongoing check, not a one-time permanent grant of trust.
Site access versus wallet authority
Extension site access, wallet connection, token allowances, and signing are distinct layers. Disconnecting does not revoke on-chain approvals; restricting domain access does not invalidate earlier signatures. Review accounts and chains and identify login messages, permits, and transfers. Interface labels cannot change authority. A gas-free off-chain signature can still have financial consequences later, so absence of an immediate fee is not evidence of harmlessness.
Updates and browser isolation
Automatic updates repair vulnerabilities but also depend on the release chain. Review notices, new permissions, and unusual behaviour. A dedicated profile reduces interactions with unrelated sites and extensions but cannot cure a compromised OS or malicious wallet. Remove unused components and investigate conflicting wallet injections. Unexpected recipients, approvals, or recovery prompts justify stopping new signatures and verifying through trusted channels rather than entering seeds into a repair popup.
Maintain an extension inventory
Inventory identifier, publisher, version, source, site permissions, connected accounts, and review date, without secrets. Question broad clipboard or all-site access for a narrow function. Following a vendor incident, inspect affected sessions, credentials, approvals, and keys rather than declaring success after a password change. Permission review limits exposure and preserves evidence; it cannot reverse completed transfers or replace checking each signing request.