Original topic illustration: ChainView BTC866 original topic diagram · ChainView BTC866 Editorial · CC BY 4.0
Classify what was exposed
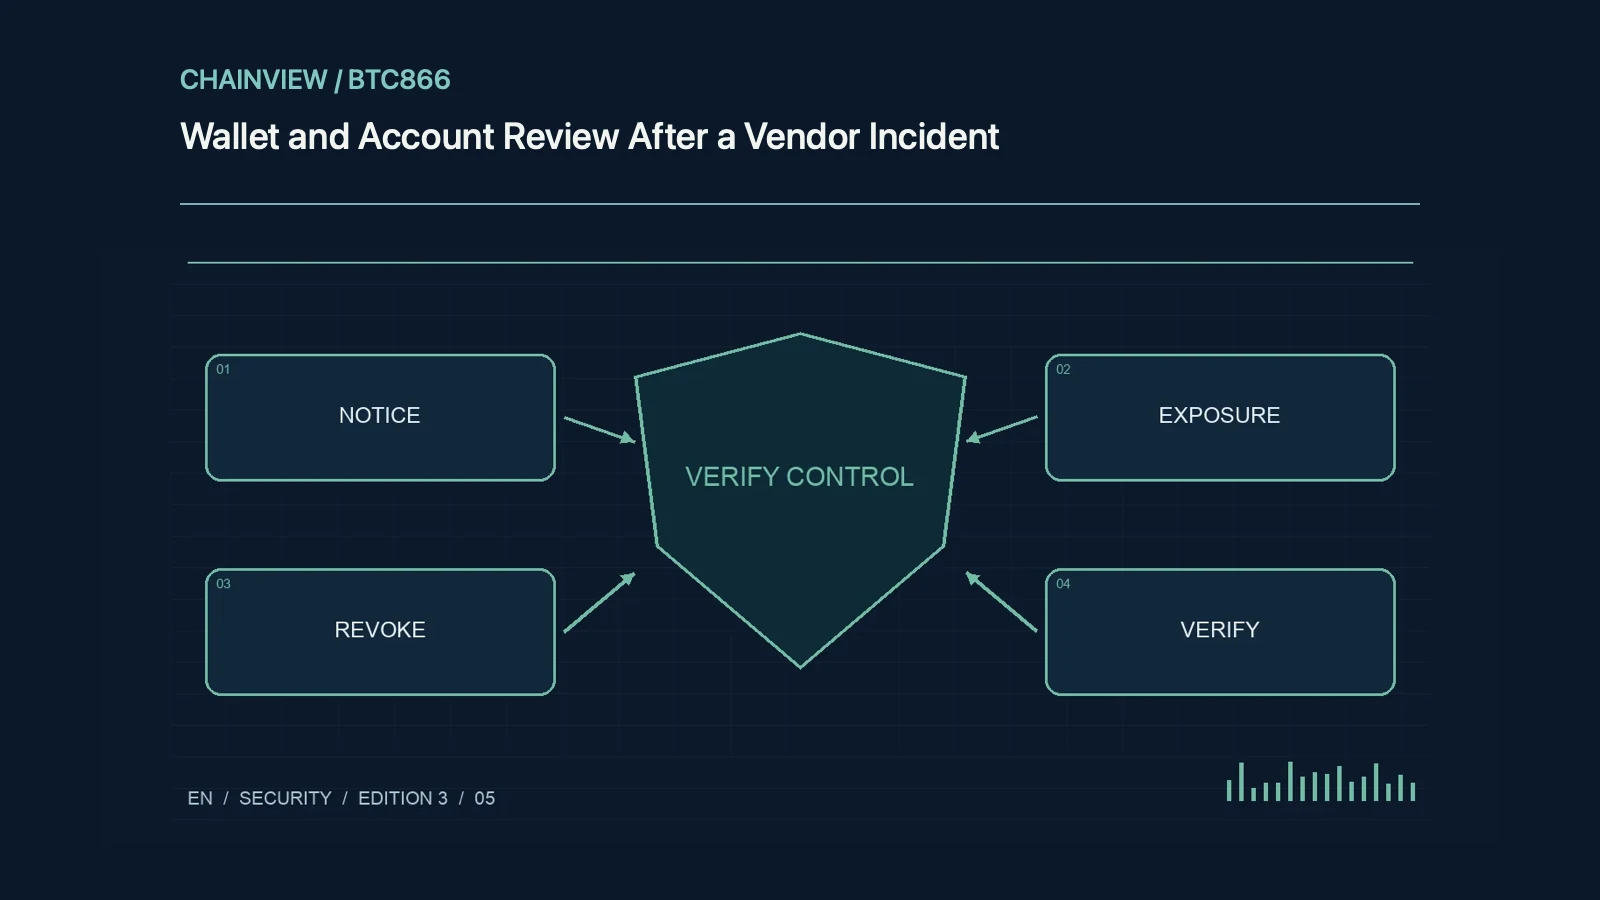
A vendor incident can expose emails, password hashes, sessions, identity documents, software, or signing keys. Responses differ. Check confirmed products, versions, dates, and impact rather than equating every data breach with key theft or every absence of withdrawals with safety. Preserve notices and account state, map affected features, and mark uncertainty. Avoid publishing personal logs or unverified loss allegations while the investigation remains incomplete.
Handle passwords, sessions, and approvals separately
Password changes may not revoke sessions, API tokens, or third-party grants. On-chain approvals and seeds are outside a central login's control; key exposure may require migration. Secure email, authenticators, and recovery paths first, then revoke unnecessary access while considering dependencies. Treat requests for recovery words, remote control, or private unfreezing payments as suspicious and verify through independently saved official channels.
Preserve evidence and migrate carefully
Keep timelines, hashes, versions, notices, and case numbers, retaining originals and redacting shared copies. If migration is warranted, verify a new wallet and address in a trusted environment and account for fees, staking, and exits. Avoid unknown cleanup scripts. Revoking an allowance can help in some cases; uninstalling an extension cannot make an exposed seed secret again. Prioritise based on actual exposure without promising guaranteed recovery.
Verify completion and keep watching
Record action, evidence, verification time, and residual risk for every item: invalid sessions, rejected tokens, or confirmed allowance changes. A password reset with a still-working old token is incomplete. Follow later advisories through bookmarks, not urgent email links. Exposed identity data can support ongoing phishing. A useful review documents irretrievable information and future dependency reductions rather than declaring every consequence solved after the immediate account works again.