Original topic illustration: ChainView BTC866 original topic diagram · ChainView BTC866 Editorial · CC BY 4.0
Keys and signatures
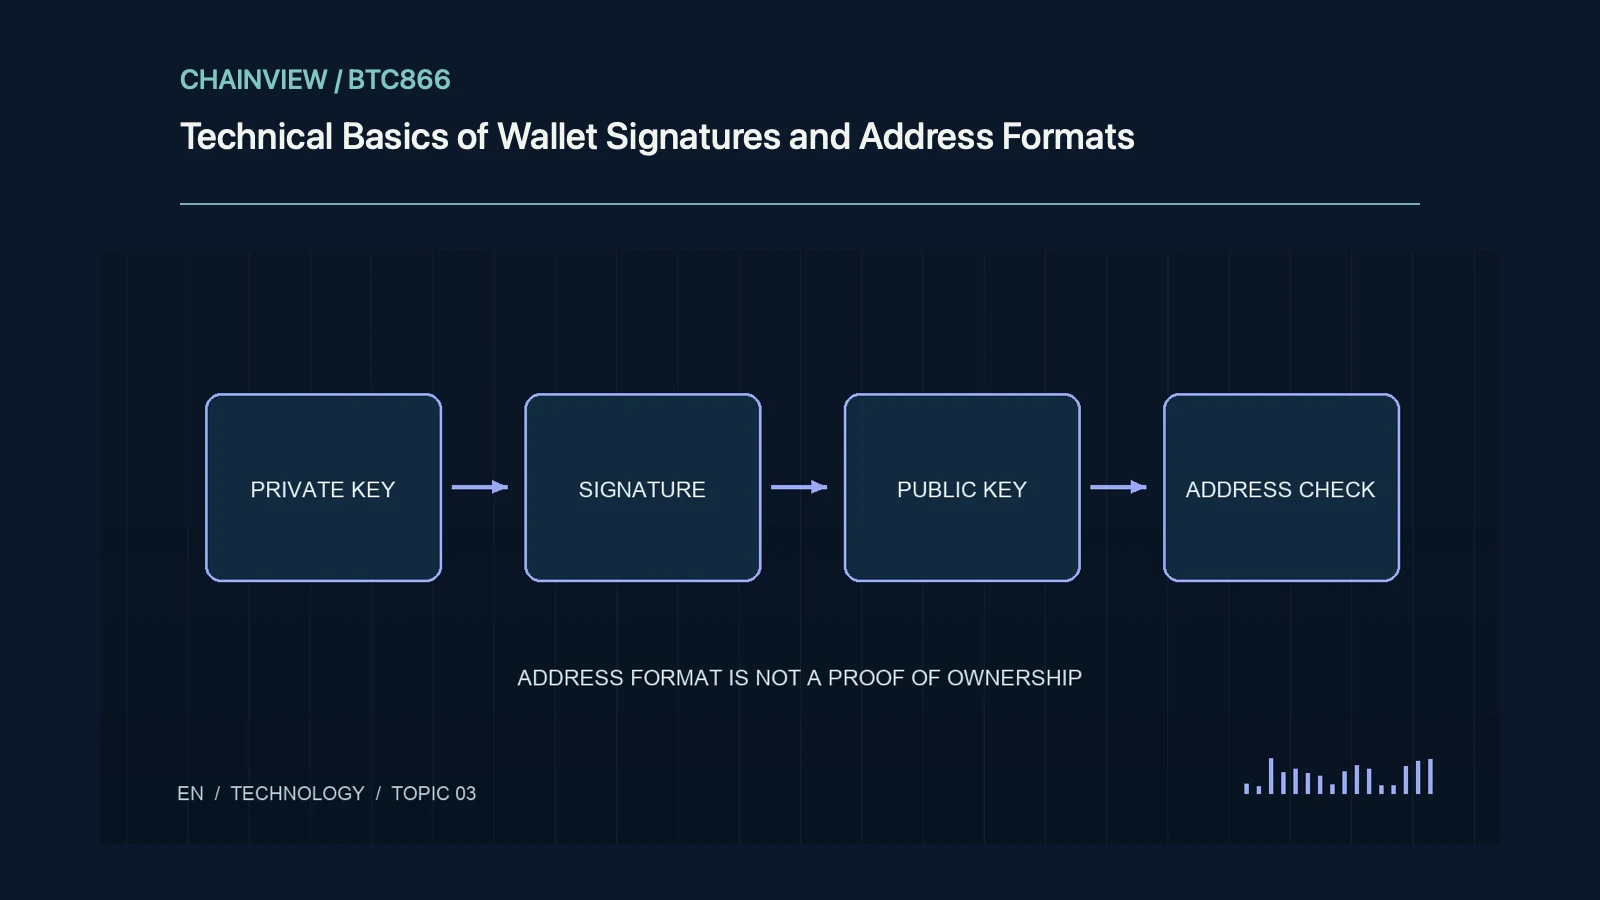
Private keys authorize spending through signatures; addresses encode receiving conditions. Wallet software manages keys and transaction construction rather than storing coins inside a device. A valid signature establishes authorization under the relevant rules, not the honesty of a recipient. Distinguish public keys, addresses, private keys, and recovery phrases before handling any of them.
Formats and network parameters
Networks can share similar-looking address formats, while one network can support several address types. Verify network parameters, testnet markers, checksums, and recipient compatibility. Checksums catch some typing errors, not malicious substitution. A perfectly valid address can belong to an attacker, so compare the complete destination on a trusted display.
Recovery phrases and derivation paths
A recovery phrase can derive multiple accounts through different paths and script types. A missing balance may reflect the wrong network, account index, path, or passphrase. A different passphrase can create a valid but unrelated wallet without an error. Practice only with trusted recovery procedures and never submit recovery material to an online checker.
Message and transaction signatures
Connection, login messages, allowances, and transfers are different actions, but signatures can have consequences. Inspect domain, chain identifier, contract, amount, and expiry. An off-chain signature may be submitted later even when no gas is paid now. Simulation and decoding help, but neither establishes that the recipient or requested authority is trustworthy.
Limits of hardware isolation
Hardware wallets isolate keys but still require reviewing the device display. A malicious site can persuade a user to approve a wrong address or broad allowance; the device cannot evaluate the business purpose. Initialize through official instructions and generate your own recovery material. A leaked seed can bypass the protection of the physical device.
Keep a compatibility test
Use an empty test wallet to record versions, networks, address types, derivation paths, and recovery outcomes. Confirm documented standards before comparing implementations. Do not repeatedly import a real seed into unfamiliar tools. A successful test validates one configuration, not a promise that all wallets and address families are mutually recoverable.
Worked review example
If the same test seed produces different addresses, compare network, path, script type, account index, and passphrase. Both results may be valid for different configurations. Reproduce the issue using an empty test seed rather than exposing a real one to unknown tools. A compatibility matrix locates the difference instead of assuming that an unfamiliar address proves wallet corruption.