Original topic illustration: ChainView BTC866 original topic diagram · ChainView BTC866 Editorial · CC BY 4.0
Establish a trusted release source
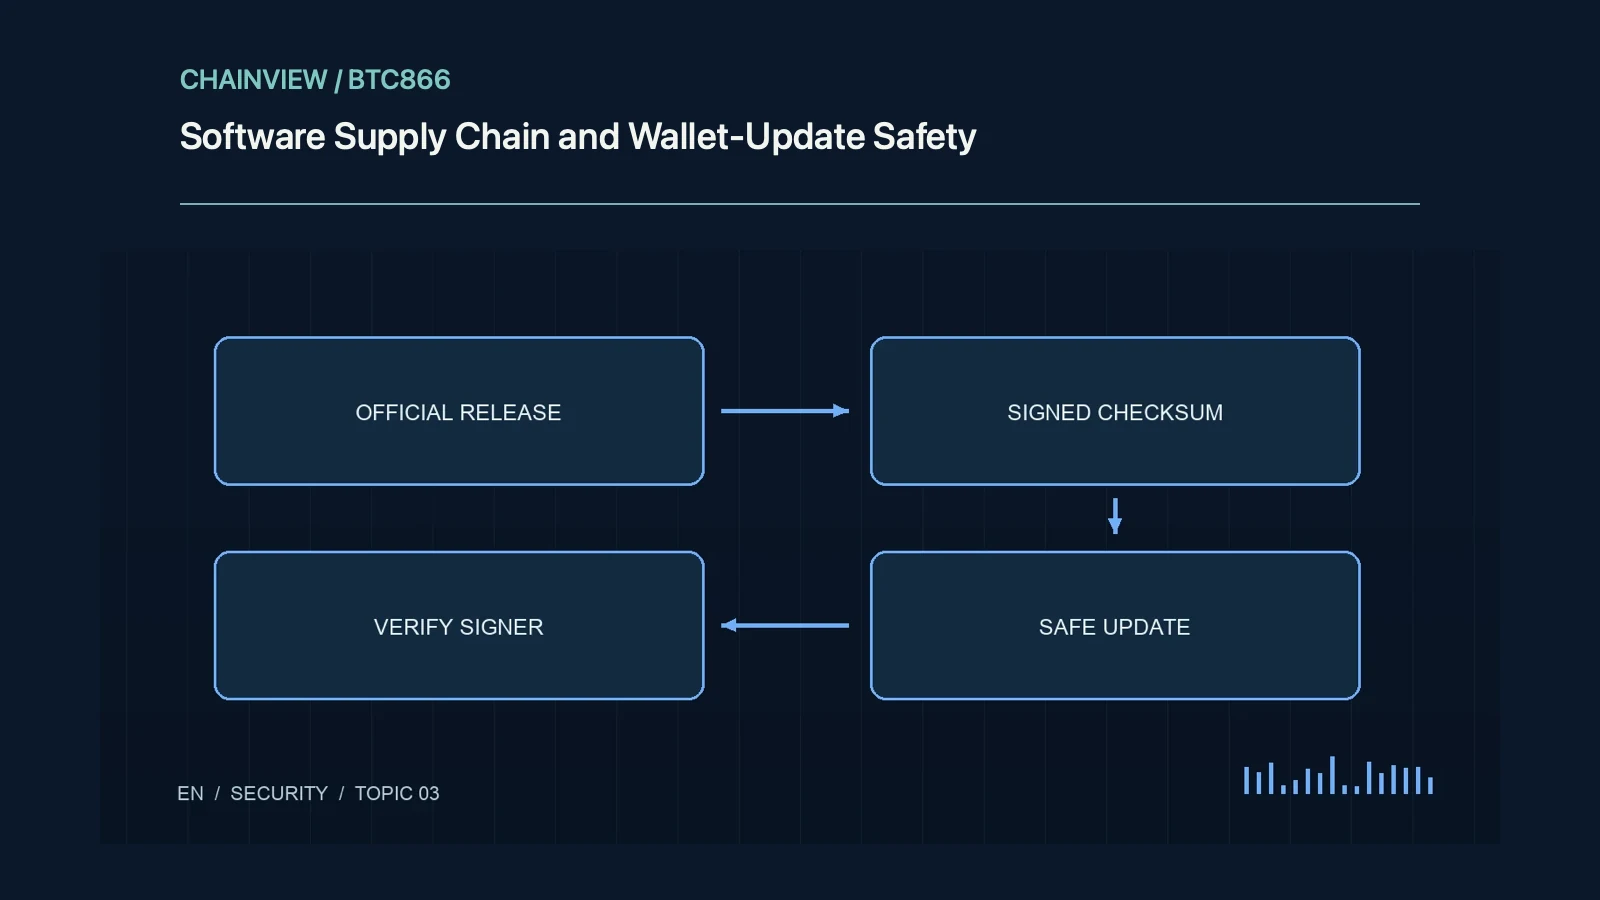
Use verified official sites, stores, or repositories rather than ads and attachments. Establish distribution channels and signing-key information beforehand. Open source does not make every download authentic; repackaging can add malicious code. Even established infrastructure can be compromised, so provenance checks should be combined with release verification.
Hashes versus signatures
Hashes compare file content; signatures bind content to a signing key. A hash from the same compromised page as the download does not independently prove authorship. Verify key fingerprints and rotation notices through documented channels. Investigate invalid signatures, unexpected keys, and mismatched release assets rather than dismissing warnings as routine inconvenience.
Release notes and permission changes
Read fixes, limitations, dependencies, and permission changes. New accessibility, screen-recording, or unrelated file access needs a clear explanation. Urgency does not authenticate an attachment. Check operating-system, database-migration, and hardware requirements before installation, especially when rollback or recovery would be difficult.
Extensions and dependencies matter
Browser extensions, dependencies, and build systems affect the surrounding environment. Limit extensions and review publishers and permissions. Developers should pin dependencies, review changes, and protect publishing credentials. Ordinary users need not execute unfamiliar terminal commands to verify safety. A trustworthy wallet cannot neutralize every malicious program running on the same device.
Rollback and recovery conditions
Check backups and data-format changes before upgrading. Older versions may not read migrated data and can reintroduce vulnerabilities. Firmware recovery differs from reinstalling an app. Follow device-specific instructions. Backup preparation never requires uploading the seed to an update page; that request is a serious anomaly requiring an immediate pause.
Post-update verification
Record installed version, verification result, and time. Check expected addresses, balances, and connection settings before consequential activity. Use a test environment where suitable. Preserve source details and logs for official reports without exposing secrets. A consistent maintenance process is more manageable than either indefinite obsolescence or unreviewed installation of every new release.
Worked review example
A matching hash cannot establish authorship if both file and hash page were compromised. Verify signatures against an independently established key and review release channels. Record permissions before installation and addresses afterward. Check rollback support for migrated databases. Provenance, functional checks, and recovery conditions together provide a stronger process than any single download badge.